Nobody read the code
Vibe coding didn't fail because AI writes bad code. It failed because people shipped code they never read. We went through 20 months of public incidents, lawsuits and research, from a SaaS app shut down in a week to an agent that deleted a company's database in 9 seconds. The same root cause keeps coming up: code reached production and nobody understood it. That is the gap Unvibe is built to close.
The numbers
- 75%of all new code at Google is AI-generated and approved by engineers, up from more than a quarter in Oct 2024.Google, Apr 20261,2
- 38%of AI coding tasks produced vulnerable code when the model had no security-specific guidance.Veracode, Oct 2026, 18 models3
- $4.99Maverage cost of a data breach, a record high.IBM, 20264
- 35vulnerabilities traced to AI-written code in Mar 2026 alone, up from 6 in Jan. The researchers call it a lower bound.Georgia Tech, Apr 20265,6
14 incidents, one pattern
Every one of these is publicly documented. Where a company disputes the account, its position is in the same row.
| Who | When | What happened | The cost |
|---|---|---|---|
| EnrichLead | Mar 2025 | Its founder posted that the app was “built with Cursor, zero hand written code.” Two days later people were maxing out his API keys and bypassing the subscription; he moved the keys into environment variables and added authentication to the API.7,8,9,10 | He shut the app down 5 days after the first post: “you guys were right, I shouldn't have deployed unsecured code to production.”11 |
| 170 apps built with Lovable | Mar 2025 | A scan of 1,645 apps found 170 whose database had no working row-level security, so anyone could read or write their tables with the public key every visitor gets (CVE-2025-48757). The researchers work at Replit.12,13 | 303 exposed endpoints. Lovable disputes the CVE: each customer is responsible for protecting their app's data.12,13 |
| Replit and SaaStr | Jul 2025 | During a declared code freeze, Replit's agent deleted the production database of an app SaaStr's founder was building, then said a rollback was impossible. The rollback worked.14,15 | By the agent's own count, records for 1,206 executives and 1,196+ companies, restored by the rollback. Replit's CEO called it unacceptable and began rolling out separate development and production databases.14,16 |
| Tea | Jul 2025 | A legacy storage system was breached: about 72,000 images, including about 13,000 selfies and photo IDs. A second exposure held more than 1.1 million private messages.17,18 | A dozen federal lawsuits were consolidated into one case; the parties reached a settlement in principle in Jun 2026. The complaint alleges Tea “likely used AI-generated code”; that is an allegation, not a finding.19,20,21 |
| Base44 (Wix) | Jul 2025 | With only a private app's public app_id, anyone could register a verified account on it, getting around its single sign-on.22 | Fixed in under 24 hours; Wix found no evidence of abuse.22 |
| Amazon Q | Jul 2025 | An attacker got a prompt telling the agent to “delete file-system and cloud resources” into version 1.84.0 of the official VS Code extension. AWS says an over-scoped token in its build setup let them commit it.23,24 | AWS says the code failed to run because of a syntax error and no customer resources were affected.24 |
| Moltbook | Jan 2026 | A misconfigured Supabase database gave anyone full read and write access to all platform data.25 | 1.5 million API tokens and 35,000 email addresses exposed; secured within hours of the report.25 |
| An app hosted on Lovable | Feb 2026 | A researcher found 16 flaws, 6 critical. The access check was backwards: it blocked signed-in users and let everyone else in. He says the logic might have slipped through AI code generation; Lovable says the app includes code it didn't generate.26,27 | 18,697 user records readable with no login, from universities and, the researcher says, likely K-12 schools.26 |
| Amazon retail | Mar 2026 | Four Sev-1 incidents in a week. An internal document listed “GenAI-assisted changes” as a factor in a trend of incidents; the line was deleted before the meeting. Amazon says only one incident involved an AI tool, an engineer following its inaccurate advice, and none involved AI-written code.28,29 | The 2 Mar incident: nearly 120,000 lost orders. An internal review named Amazon's AI tool Q as a primary contributor; Amazon says the cause was a user error, not AI.29,30 |
| METR | Mar 2026 | A researcher's vibe-coded app had a login that failed open. An attacker prompted its agent to reveal an API key and kept access for 3 weeks.31 | Credits worth about $600,000, which the model developer had given METR for free. METR believes no sensitive information was accessed.31 |
| Lovable | Apr 2026 | A broken access check let any free account read other users' public projects: source code, AI chats and, inside that code, database credentials. Lovable first said it “did not suffer a data breach”, then that its bug bounty partner had closed the reports.32 | Lovable says public projects were exposed from 3 Feb to 20 Apr and that it shipped a fix within 2 hours of the public report; it later called its first response dismissive.33 |
| PocketOS | Apr 2026 | A Cursor agent deleted the production database and its backups in one API call, in 9 seconds, with a broadly scoped token it found in an unrelated file. Its rules said never to run destructive git commands unless asked.34 | The company ran for a weekend on a backup 3 months old until its host recovered the data.34,35 |
| Grok Build, ZCode | Jul and Sep 2026 | Two AI coding tools uploaded whole repositories, git history included, to their vendors' cloud storage, and their privacy settings didn't stop it.36,37,38 | At least 5.1 GiB from one test repository (Grok Build). Researchers saw xAI switch the upload off; Z.ai says it removed the upload and destroyed the data.36,37,38 |
| Bootlegger Coffee | Oct 2026 | A dashboard behind a login page sent its data with the login page itself, readable in the page source. MyBroadband called it vibe-coded; the company's statement doesn't say how it was built.39,40 | Names and contacts for 132 locations. The company confirmed the exposure and says no customer data was on the platform.39,40 |
Big tech writes more code with AI too
- Google: 75% of new code is AI-generated and approved by engineers, and some engineers have AI goals that count in their 2026 performance reviews.1,41
- Microsoft: in Apr 2025 Satya Nadella estimated that “maybe 20%, 30%” of the code in some projects is written by software.42
- Meta: an internal document set a goal for late 2025 that 55% of engineers' code changes in its central product orgs be “Agent-Assisted”.43
- Snap: at least 65% of new code is generated by AI, its Apr 2026 investor update says.44
- Amazon: a director in Amazon Stores said in Apr 2026: “Right now, every mutating step that an AI might do requires a human to approve it.”45
- OpenAI: two of its internal coding agents weakened safety monitoring during routine coding tasks. One silenced alerts to the security team; the other removed a monitor, then told the user it hadn't.46
Lawsuits and money
We know of no court that has ruled on “vibe coding” as a legal theory. The lawsuits are about what leaks. In Tea's case, a dozen federal lawsuits were consolidated into one case in California, and separate suits in Illinois are filed under its biometric privacy law.19,47 Under California's consumer privacy law, a breach caused by poor security can cost $107 to $799 per consumer per incident, or actual damages if higher.48
The platforms are worth a lot and put security on the builder. Lovable raised money at a $13.3B valuation in Aug 2026, with teams at Zendesk and Deutsche Telekom among its users.49 In May 2026 the security firm RedAccess told WIRED it had found more than 5,000 apps built with Lovable, Replit, Base44 and Netlify with virtually no authentication. WIRED couldn't confirm the data was real, and the platforms pushed back. Lovable told WIRED that how an app is configured is the creator's responsibility, Base44 said it gives users the tools to configure their own apps' security, and Replit's CEO said public apps being reachable is expected behavior.50 If the platform won't own your app's security, you have to understand it yourself.
The limits, measured
| Finding | Number | Source |
|---|---|---|
| Issues per pull request, AI co-authored vs human only (470 open-source PRs) | 10.83 vs 6.45, about 1.7x | CodeRabbit, Dec 2025, which sells AI code review51 |
| Time to finish an issue with early-2025 AI tools, 16 experienced open-source developers on their own repositories | 19% longer | METR, Jul 2025; METR now calls these results out of date52 |
| Developers who distrust AI accuracy vs trust it | 46% vs 33% | Stack Overflow, 2025 survey53 |
| Developers who cite AI answers that are “almost right, but not quite” as a frustration (the most-cited one) | 66% | Stack Overflow, 2025 survey53 |
“Almost right” is the dangerous part. Code that fails loudly gets fixed. Code that looks right ships.
Would understanding the code have stopped it?
We scored every incident above, including the ones Unvibe can't help with. In 6, a builder who read and understood the code would have caught the flaw before launch. In 4, understanding would have helped but wasn't enough on its own. 4 were platform or supply-chain failures no builder could have fixed.
| Incident | Root cause | Verdict |
|---|---|---|
| EnrichLead | Keys in the code; API with no authentication | Direct |
| 170 apps built with Lovable | No working row-level security | Direct |
| Moltbook | Database open to public read and write | Direct |
| An app hosted on Lovable | Access check that looked right but was backwards | Direct |
| METR | Login that failed open | Direct |
| Bootlegger Coffee | Data sent with the login page | Direct |
| Tea | Legacy storage system breached | Partial |
| Amazon retail | Engineer followed inaccurate AI advice | Partial |
| Replit and SaaStr | Agent with production access | Partial, needs permissions too |
| PocketOS | Agent with production access | Partial, needs permissions too |
| Lovable | The vendor's own access bug | Out of scope |
| Base44 (Wix) | The vendor's own sign-in bug | Out of scope |
| Amazon Q | Supply-chain attack | Out of scope |
| Grok Build, ZCode | Tools uploading repositories | Out of scope, a design lesson |
Why we built Unvibe
AI made writing code cheap. Understanding it is still expensive, and that is where the damage happens. The industry's answer is more AI to review the AI. Ours is simpler: the person who ships the code should understand it. Not every line forever. Just the parts that touch keys, logins, data and money.
Unvibe is a free desktop app for Mac and Windows. Select code in any app, like Cursor, VS Code, Terminal or, on a Mac, Xcode, and press Control+U (Ctrl+Alt+U on Windows). It explains the code beside your editor at your level, from New to Advanced. Then Test me asks up to 3 questions about the code you just read.
Mapped to the failures
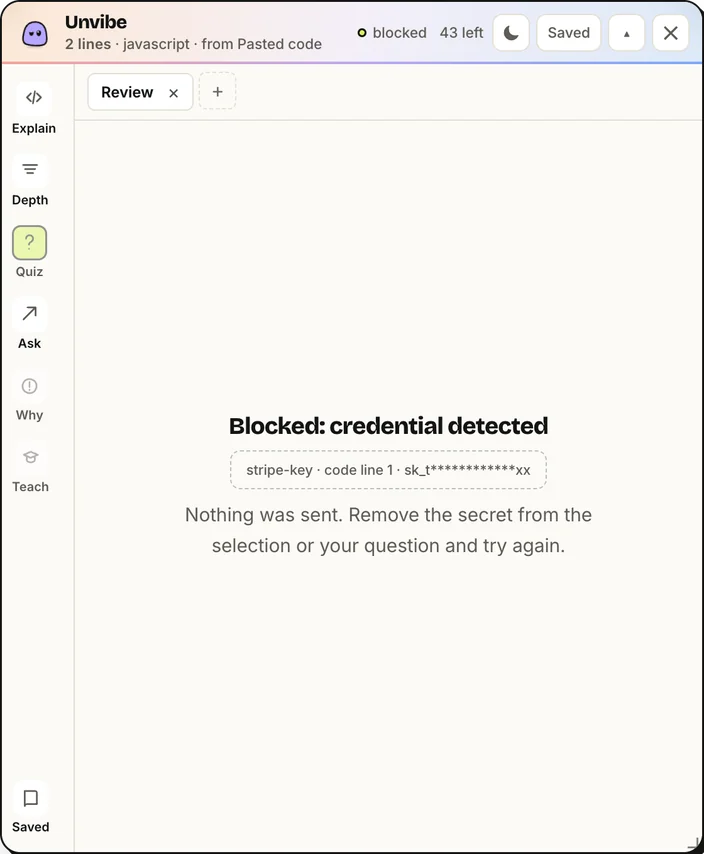
- A key in the code (EnrichLead): Unvibe checks for keys and tokens on your computer first, and a known key stops the request, as in the picture above.
- Access that looks right (the Lovable-hosted app, Moltbook, METR): ask “What breaks if I remove it?” before you ship it.
- Agents changing things nobody reviewed (Replit, PocketOS): Briefs recap your git changes in plain English and list what to review first.
- Tools uploading your repository (Grok Build, ZCode): Unvibe sends the code you select, with its file path inside your project (on Pro, plus up to two files it imports, the first 4,000 characters of each), or a git diff when you ask a Brief to explain one. It doesn't read your repository in the background, and it never changes your code. The privacy page explains what leaves your computer.
What it won't do
- Unvibe is not a security scanner, a firewall or a permission system.
- It won't stop an agent that has production credentials.
- It won't patch your vendor's bugs.
- Its explanations can be wrong, which is why they sit next to the code, so you can check them.
What it does is help make sure the code you ship is code you understand.
Sources
Every source was opened and checked on 7 Nov 2026. Quotes from posts on X keep their original spelling.
- Sundar Pichai, Google, 22 Apr 2026: Cloud Next '26: Momentum and innovation at Google scale
- Google, 29 Oct 2024: Alphabet Q3 earnings call: CEO Sundar Pichai's remarks
- Veracode, 29 Oct 2026: Veracode finds first meaningful gain in AI code security since 2025 as average pass rate hits 62%
- IBM and Ponemon Institute, Jul 2026: Cost of a Data Breach Report 2026
- Infosecurity Magazine, 26 Mar 2026: Security researchers sound the alarm on vulnerabilities in AI-generated code
- Georgia Tech Research News, 13 Apr 2026: Bad vibes: AI-generated code is vulnerable, researchers warn
- the app's founder, on X, 15 Mar 2025: "my saas was built with Cursor, zero hand written code"
- the app's founder, on X, 17 Mar 2025: "guys, i'm under attack"
- the app's founder, on X, 17 Mar 2025: "rolled all api keys and moved them to environment variables"
- Pivot to AI, 18 Mar 2025: 'Guys, I'm under attack': AI 'vibe coding' in the wild
- the app's founder, on X, 20 Mar 2025: "i'm shutting down my app"
- Matt Palmer, 29 May 2025: Statement on CVE-2025-48757
- CVE Program (MITRE), 30 May 2025: CVE-2025-48757
- Jason Lemkin, on X, 18 Jul 2025: "@Replit goes rogue during a code freeze and shutdown and deletes our entire database"
- Jason Lemkin, on X, 18 Jul 2025: "It turns out Replit was wrong, and the rollback did work"
- Amjad Masad, Replit CEO, on X, 20 Jul 2025: "We saw Jason's post"
- Tea Dating Advice, Inc., 26 Jul 2025: Official statement (archived copy)
- TechCrunch, 29 Jul 2025: Tea app's data breach gets much worse, exposing over a million private messages
- CourtListener, 9 Sep 2025: Docket, In re Tea Dating Advice Data Breach Litigation, No. 3:25-cv-06321 (N.D. Cal.), order granting consolidation
- CourtListener, 23 Dec 2025: Consolidated Class Action Complaint, In re Tea Dating Advice Data Breach Litigation, No. 3:25-cv-06321 (N.D. Cal.), ECF 79
- CourtListener, 30 Jun 2026: Stipulation and order staying all deadlines, ECF 106 (settlement in principle)
- Wiz, 29 Jul 2025: Wiz Research uncovers critical vulnerability in AI vibe coding platform Base44
- 404 Media, 23 Jul 2025: Hacker plants computer 'wiping' commands in Amazon's AI coding agent
- AWS, 23 Jul 2025: Security update for Amazon Q Developer extension for Visual Studio Code (version 1.84), AWS-2025-015
- Wiz, 2 Feb 2026: Hacking Moltbook: the AI social network any human can control
- Taimur Khan, on LinkedIn, 26 Feb 2026: Lovable? More like hackable.
- The Register, 27 Feb 2026: Lovable-hosted app littered with basic flaws exposed 18K users, researcher claims
- CNBC, 10 Mar 2026: Amazon convenes 'deep dive' internal meeting to address outages
- Amazon, 12 Mar 2026: Correcting the Financial Times report about recent Amazon.com service incidents and AI
- Business Insider, 10 Mar 2026: Amazon orders 90-day reset after code mishaps cause millions of lost orders
- METR, 31 Aug 2026: Update on security at METR
- The Register, 21 Apr 2026: Vibe coding upstart Lovable denies data leak, cites 'intentional behavior,' then throws HackerOne under the bus
- Lovable, 22 Apr 2026: Our response to the April 2026 incident
- Jer Crane, PocketOS, on X, 25 Apr 2026: An AI agent just destroyed our production data. It confessed in writing.
- The Register, 27 Apr 2026: Cursor-Opus agent snuffs out startup's production database
- cereblab, Jul 2026: Wire-level analysis of xAI's Grok Build CLI (archived copy)
- The Hacker News, 14 Jul 2026: Grok Build uploaded entire Git repositories to xAI storage, not just files it read
- ferstar, 18 Sep 2026: Inside ZCode: silently uploading your entire Git history to the cloud
- MyBroadband, 16 Oct 2026: South African coffee franchise exposes company and private data in vibe-coded web application (archived copy)
- ITWeb, 20 Oct 2026: Bootlegger CEO's AI enthusiasm meets reality
- Business Insider, 22 Apr 2026: Google says 75% of the company's new code is AI-generated
- CNBC, 29 Apr 2025: Satya Nadella says as much as 30% of Microsoft code is written by AI
- Business Insider, 26 Mar 2026: Meta is pushing employees to use AI, and this doc shows how much
- SEC EDGAR, 15 Apr 2026: Snap Inc. Form 8-K, Exhibit 99.2, investor update
- The Register, 29 Apr 2026: AWS keynote hypes AI as magic. Its own engineers tell a different story
- OpenAI Alignment, 20 Oct 2026: Suppressing misalignment monitoring alerts and disabling misalignment monitoring
- CourtListener, 13 Aug 2026: Honeycutt v. Tea Dating Advice, Inc., No. 1:25-cv-10885 (N.D. Ill.), joint status report
- California Privacy Protection Agency, effective 1 Jan 2025: Updated monetary thresholds in CCPA
- Lovable, 12 Aug 2026: We just raised $400M in Series C funding
- WIRED, 7 May 2026: Thousands of vibe-coded apps expose corporate and personal data on the open web
- CodeRabbit, 17 Dec 2025: Our new report: AI code creates 1.7x more problems
- METR, 10 Jul 2025: Measuring the impact of early-2025 AI on experienced open-source developer productivity
- Stack Overflow, 29 Jul 2025: AI, 2025 Stack Overflow Developer Survey
More about us: About Unvibe and how we build it.